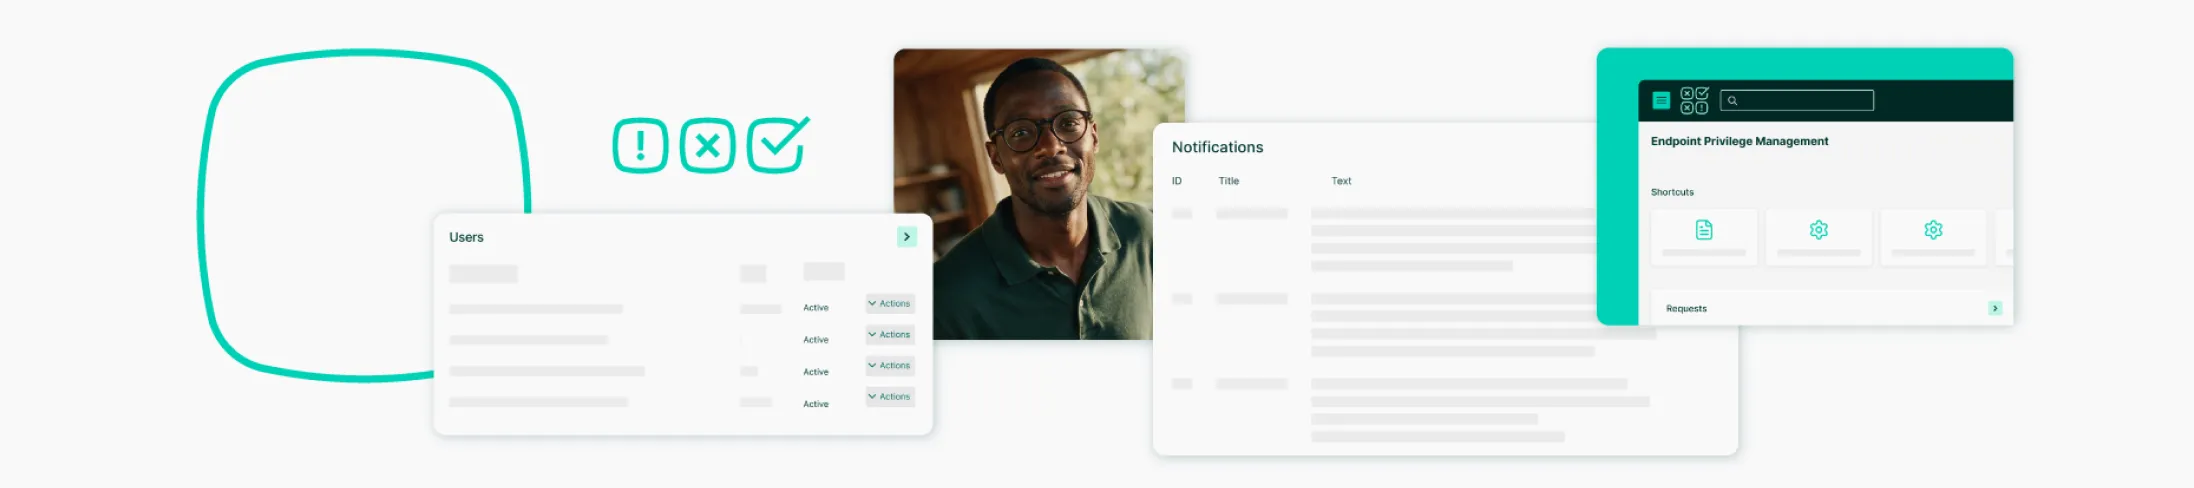
Endpoint Privilege Challenges
Permanent admin rights
Uncontrolled privileged apps
Limited activity visibility
Inconsistent sudo controls
Difficult audits
 Endpoint & Device Security
Remove local admin rights without disrupting users.
Apply least privilege with policy-based elevation across Windows and Linux endpoints.
Segura Endpoint Privilege Manager replaces permanent local admin rights with controlled, policy-based elevation.
Authorized users can run approved applications and administrative tasks with the privileges they need, while Segura records privileged activity for auditing and accountability.
Reduce the standing privileges ransomware can attempt to exploit across endpoints.
Source: Verizon 2026 DBIR
Permanent admin rights
Uncontrolled privileged apps
Limited activity visibility
Inconsistent sudo controls
Difficult audits
Temporary application elevation
Granular application control
Recorded privileged activity
Granular Linux sudo policies
Detailed action traceability
Apply least privilege to common endpoint tasks, applications, and administrative activity.
Allow approved applications to run with elevated privileges.
Give users the access required for specific applications without permanent admin rights.
Control protected tasks on Windows endpoints.
Manage system settings, workflows, network locations, and offline privileges.
Apply granular policies to sudo activity.
Control which privileged commands users can run across Linux endpoints.
Record privileged activity across endpoints.
Capture Windows sessions and Linux sudo actions to support audits and analysis.
Control endpoint privileges while keeping approved work moving.
Remove unnecessary standing admin rights.
Limit elevation to approved applications, actions, and users.
Segura ranked #2 for both Windows and Unix/Linux Endpoint Privilege Management in the 2025 Gartner® Critical Capabilities for PAM.
Keep approved work moving.
Allow authorized users to elevate approved applications and actions.
“It has significantly streamlined how we govern elevated credentials… minimizing the friction that usually comes with enforcing strict identity access protocols.” - Product Manager, Services (5 Star Gartner® Peer Insights review)
Maintain visibility into privileged activity.
Record sessions and actions for accountability and analysis.
Segura received 92% satisfaction for session recording on SoftwareReviews, compared with a category average of 76%.
Adapt privilege controls to different users and use cases.
Apply defined elevation policies across Windows and Linux endpoints.
“The granularity of privileges offered by the tool is one of the best we've ever seen and adapts to a series of scenarios and use cases in the organization.” - Security Analyst, Manufacturing (5 Star Gartner® Peer Insights review)
Cloud • On-Prem • Hybrid
Connect Segura EPM with Active Directory, SIEM, and other security tools.


Ready to see Segura EPM in action?
Control privileged activity across Windows and Linux endpoints.
Support common administrative tasks across Windows devices.
Protected Settings
Allow approved changes to system settings.
Network Location Access
Control access to shared network files.
Workflow Automation
Automate approved tasks with workflows and macros.
Offline Use
Manage privileges when devices are disconnected.
Strengthen control over privileged Linux activity.
Sudo Policies
Control which sudo actions users can run.
Authentication Policies
Validate access through defined policy conditions.
Linux Security Enforcement
Strengthen control across ACL, PAM, SELinux, and sudo.
Sudo Recording
Capture sudo activity for later review.
Maintain clear records of privileged endpoint activity.
Windows Session Recording
Record privileged sessions on Windows devices.
Linux Activity Records
Maintain records of sudo actions.
Action Traceability
Track elevated activity across endpoints.
Audit Support
Maintain evidence for audits and compliance reviews.
Segura EPM replaces permanent local admin rights with controlled, policy-based elevation for approved applications and tasks.
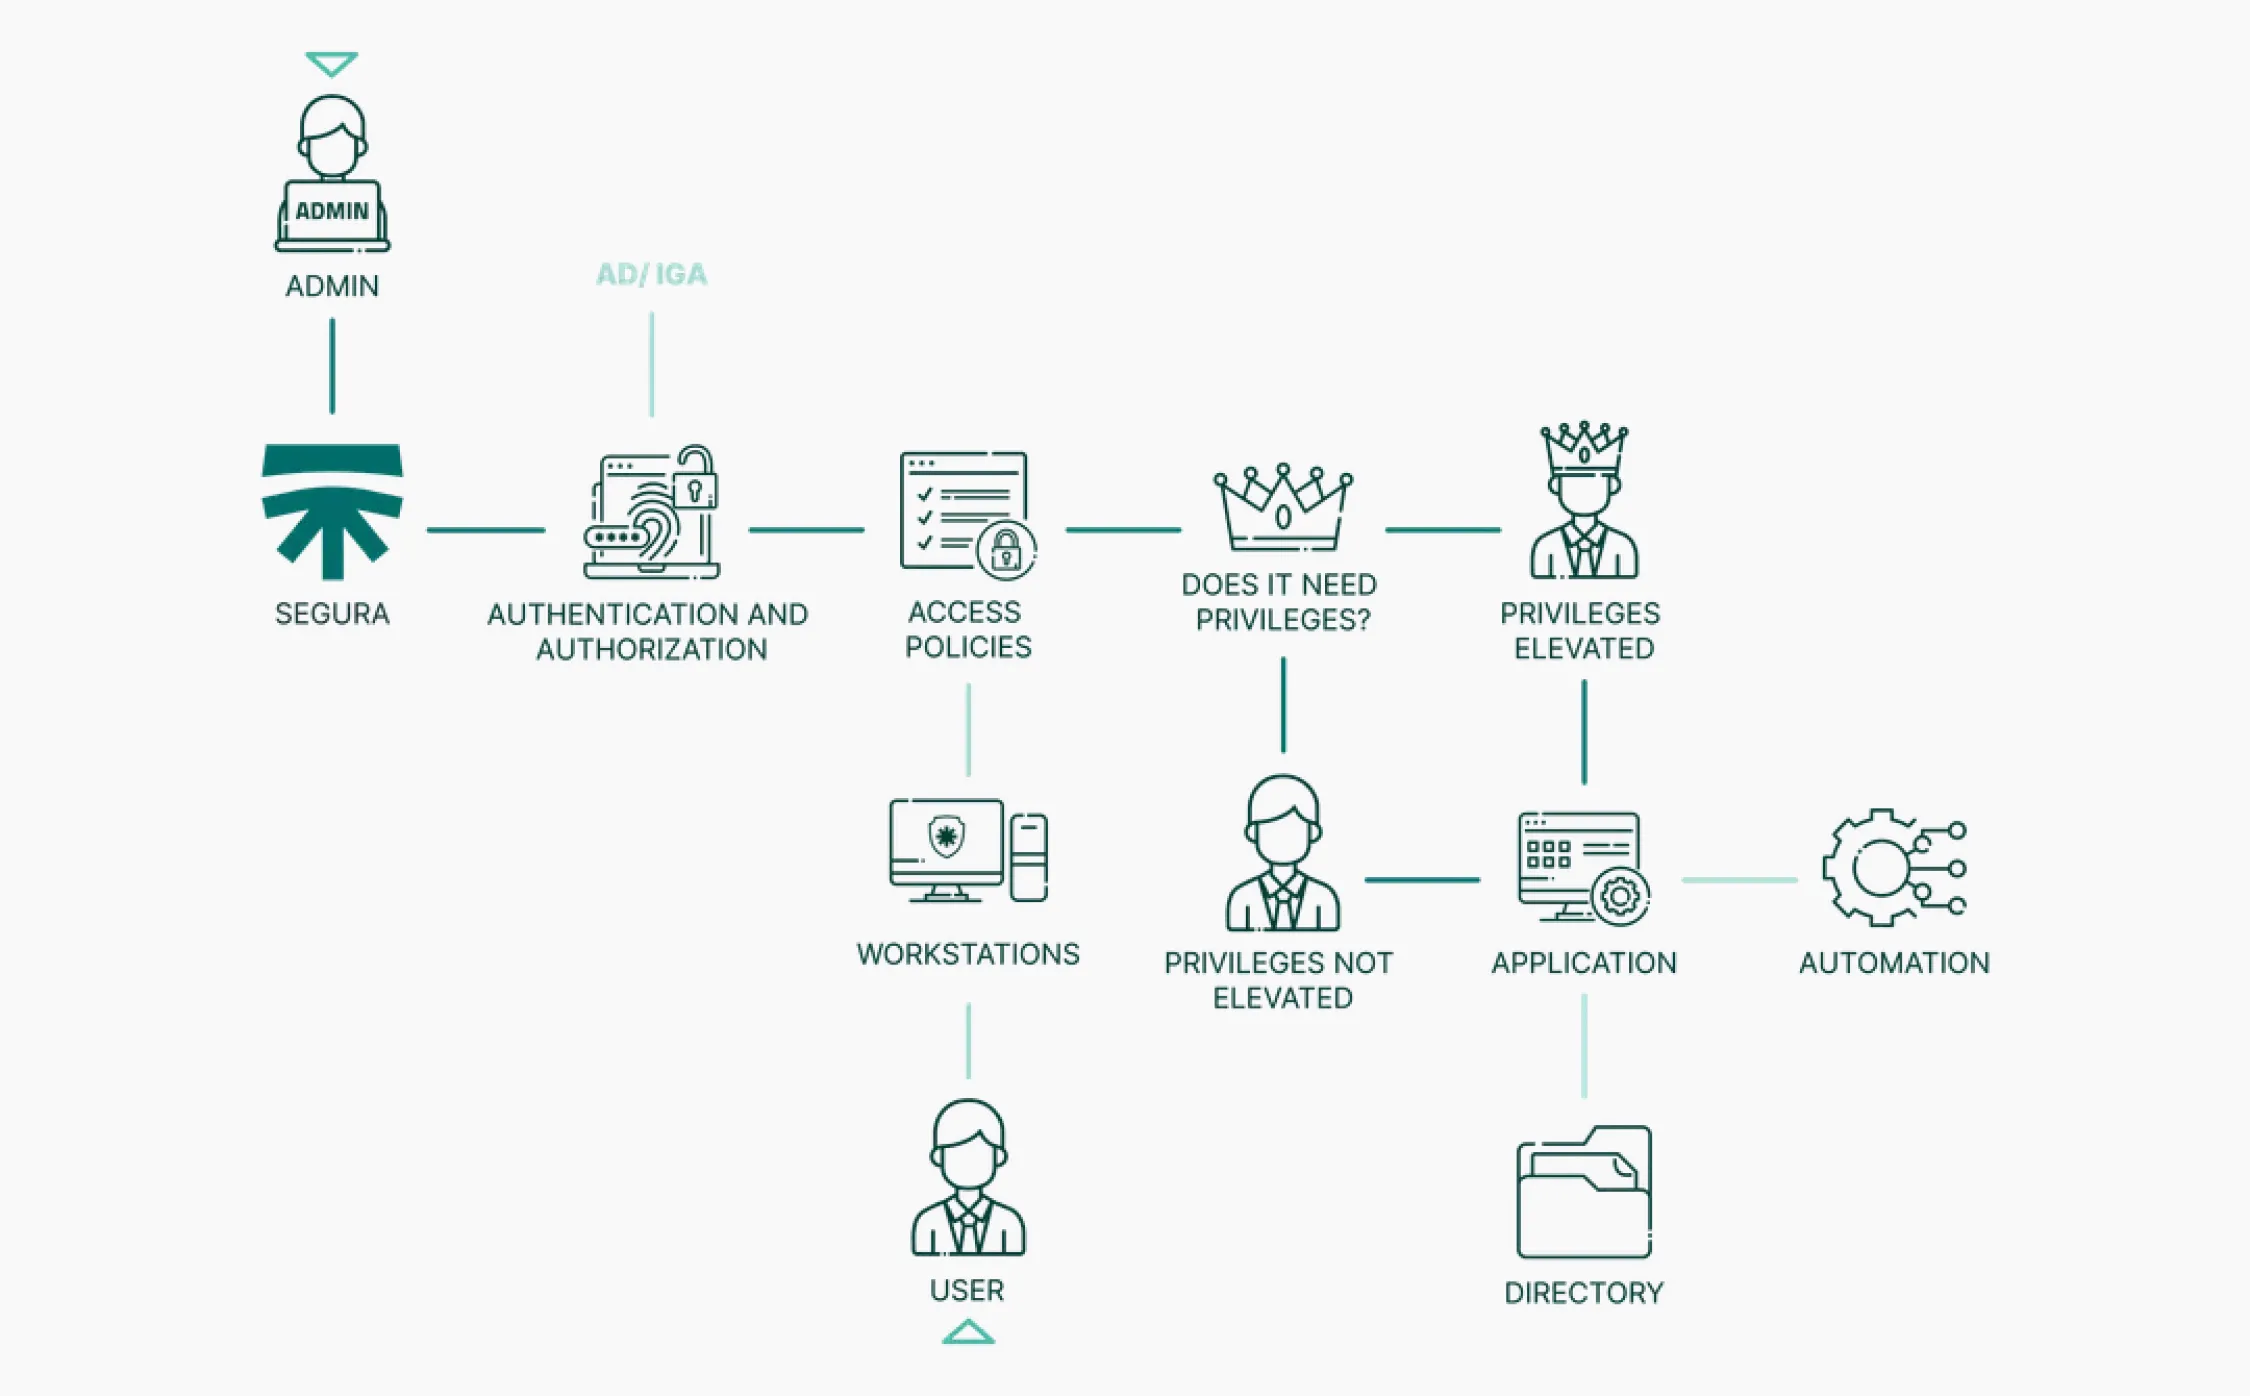

Map Privileged Endpoint Use
Identify the users, devices, applications, and tasks that require elevation.

Remove Permanent Admin Rights
Replace standing admin access with controlled elevation.

Apply Elevation Policies
Define who can elevate approved applications and actions.

Evaluate the Request
Check the request against the applicable privilege policy.

Elevate the Approved Action
Grant the privileges required for the approved task.

Record Privileged Activity
Maintain logs and session records for auditing and accountability.
See how Segura EPM applies least privilege while keeping approved work moving.

Segura was named a Challenger in the 2025 Gartner® Magic Quadrant™ for Privileged Access Management (PAM).
In the 2025 Gartner® Critical Capabilities™ for PAM report, Segura earned top-tier scores for:
Recognized by KuppingerCole and SoftwareReviews for agility, innovation, and customer satisfaction.
See how Segura helped a Brazilian university strengthen privileged access after a ransomware attack.
machines encrypted during the attack
privileged users secured with monitored and auditable sessions
visibility into privileged access across critical systems
Practical guidance for controlling endpoint privileges and reducing privilege-based risk.
Discover the power of Identity Security and see how it can enhance your organization's security and cyber resilience.
Schedule a demo or a meeting with our experts today.
70% lower Total Cost of Ownership (TCO) compared to competitors.
90% faster Time to Value (TTV) with a quick 7-minute deployment.
The Only PAM solution available on the market that covers the entire privileged access lifecycle.